Your departments define the rules.
Who enforces them?
Cyber sets controls. HR sets policies. Compliance monitors frameworks. But when something goes wrong — none of them are equipped to investigate. That's the enforcement gap. OrcheSight closes it.
The Readiness Gap
Schellman, 2026 State of AI Governance — 500+ US enterprise leaders

The Next Executive Role
Chief Information Enforcer — one leader for all digital enforcement. OrcheSight makes it possible.
The Structural Problem
Every department defines rules for its domain. None of them are built to investigate when those rules are broken. The enforcement function doesn't exist — until now.
Cyber Security
Security controls, threat detection, incident response playbooks
Fails at forensic investigation when a breach actually happens. SIEM alerts pile up; no one builds a case.
HR
Workplace policies, codes of conduct, disciplinary procedures
Investigates misconduct in spreadsheets. No chain of custody, no cross-department visibility.
Privacy
Data protection rules, GDPR/CCPA compliance, consent frameworks
Cannot conduct a proper investigation when a violation surfaces. Opens a ticket, not a case.
Compliance
Regulatory frameworks, audit schedules, policy monitoring
Detects a violation and opens a ticket — not an investigation. Evidence stays in the monitoring tool.
Legal
Litigation hold procedures, discovery obligations, privilege rules
Evidence scattered across 5 tools and 3 departments. Assembling a case file takes weeks.
Separate who defines the rules from who enforces them
Today, every department both defines controls and tries to enforce them. That means six separate teams running investigations in six separate tools with six broken chains of custody.
OrcheSight enables a dedicated enforcement function: departments continue to define their controls, but investigation, evidence management, and reporting flow through one team on one platform.
See how the model worksConsolidate resources. Increase effectiveness.
Today, enforcement work lands on whoever is nearest — HR managers running investigations in spreadsheets, security analysts assembling evidence manually, compliance officers compiling audit packages by hand. None of them were hired to investigate, and none of them were given the tools for it.
The enforcement model changes this. You take the investigative burden off each department and consolidate it into one professional team with the right tools. The people freed up go back to what they were hired for — managing security, running HR, overseeing compliance.
OrcheSight replaces fragmented tools over time — not everything on day one, but with measurable ROI at each step. Fewer licenses, fewer duplicate efforts, better outcomes.
Consolidate tools
Replace disconnected tools with one platform. Fewer licenses, fewer integrations, fewer vendor relationships.
Free department resources
HR, Cyber, and Compliance staff stop running investigations and return to their core responsibilities.
Professional enforcement team
A smaller, dedicated team with the right methodology handles enforcement across every domain — more effective, more defensible.
Measurable ROI at each step
Start with one module. Replace one tool. Free one set of resources. Expand as value is proven — not as a leap of faith.
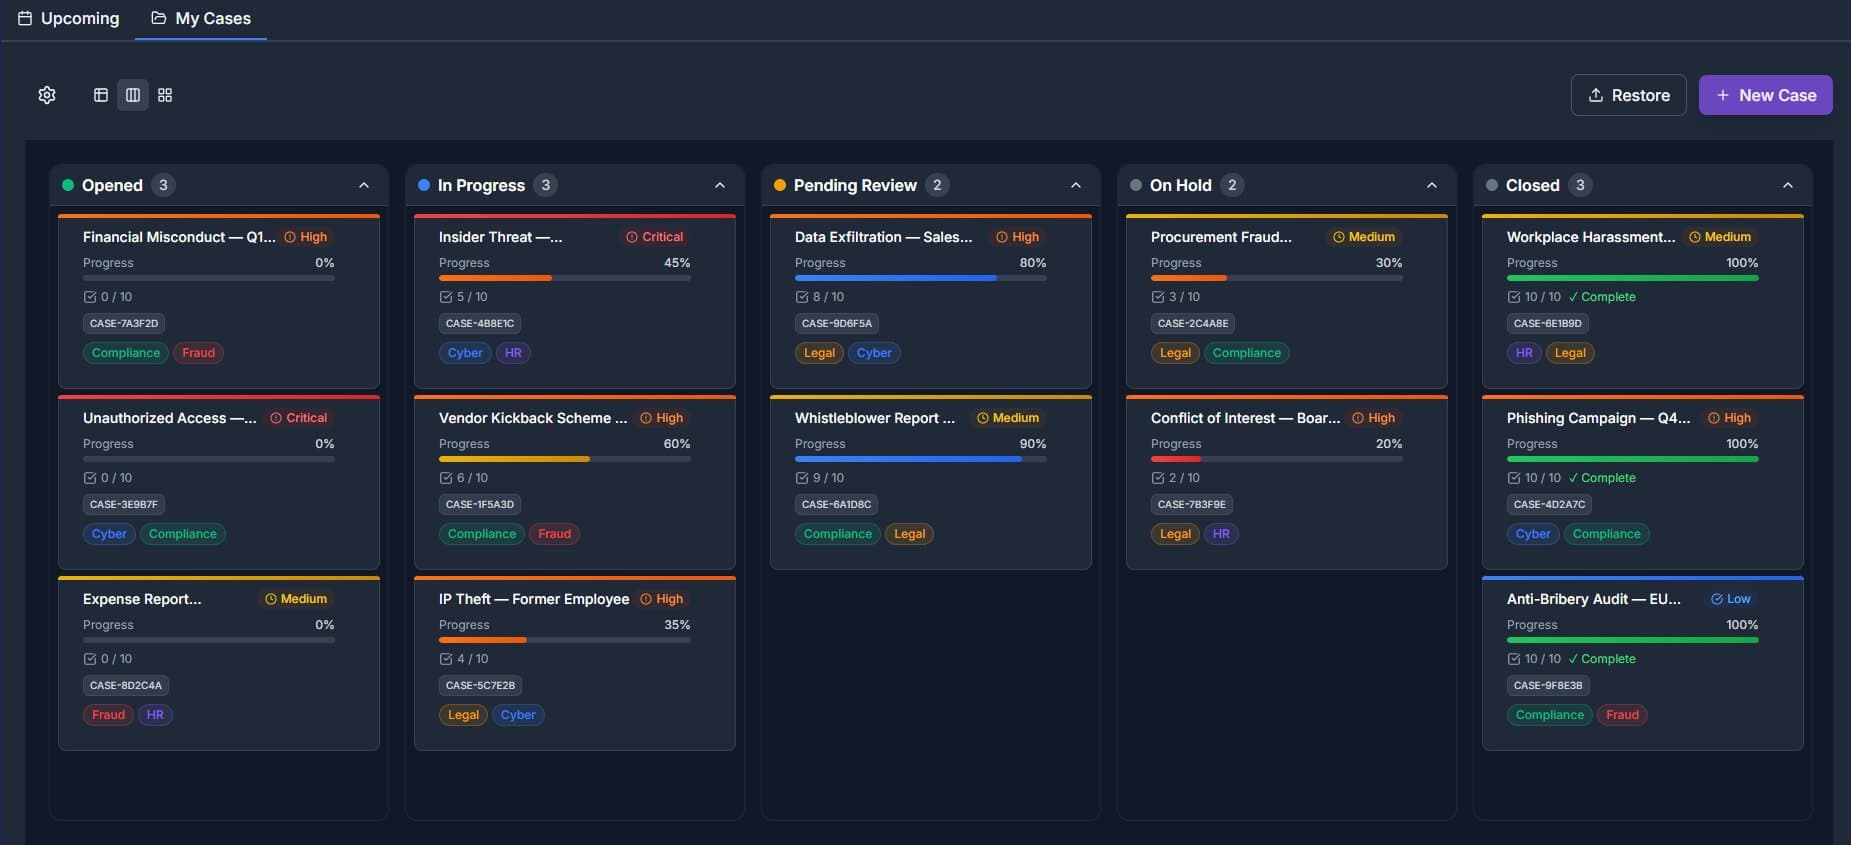
Unified case management across departments
HR, Cyber, Legal, and Compliance investigations share a single case record. Every action is logged, timestamped, and attributed. Evidence chain of custody is maintained from collection through disposition.
Built for your environment
Government agencies, law firms, financial institutions, and enterprises face different regulatory pressures — but share the same fragmentation problem. OrcheSight adapts to each.
Government & Law Enforcement
“Classified evidence spread across disconnected systems. No unified chain of custody. Investigations stall at department handoffs.”
Air-gapped deployment with full sovereignty. Evidence from body cameras, CCTV, and digital sources processed in one pipeline. Court-ready chain of custody from day one.
Legal & eDiscovery
“Document review takes weeks and costs hundreds of thousands. Evidence collected in one tool, reviewed in another, produced in a third. Chain of custody gaps everywhere.”
Collection through production in one platform. AI-assisted privilege detection, relevance ranking, and PII redaction reduce review time and cost. No tool-to-tool handoffs.
Financial Services & Compliance
“Compliance monitoring detects a violation — then a separate team opens a separate investigation in a separate tool. Evidence assembled manually for regulators.”
When a policy violation is detected, it becomes an investigation automatically — same platform, same evidence chain. Audit packages generated for GDPR, SOX, CCPA.
Enterprise & HR
“HR runs a misconduct investigation in spreadsheets. Legal runs a parallel investigation in their own system. Neither knows what the other found. Audit trail is incomplete.”
One case record shared across HR, Legal, Cyber, and Compliance. Every action logged and attributed. Role-based access ensures need-to-know controls while maintaining a single source of truth.
8 Modules. One Platform.
Each module handles a specific function. All share one evidence chain and one audit trail.
Forensic investigation practice across government, legal, and financial sectors.
Deduplication, OCR, entity extraction, classification, relevance ranking — automated end-to-end.
Collection, Investigation, Intelligence, Review, IR, Interview Room, and Compliance.
Deployment Options
OrcheSight runs wherever your data needs to stay.
SaaS on Azure
Fully hosted. Infrastructure managed by OrcheSight.
Air-Gapped On-Premises
Complete platform deployed inside your perimeter. Zero external dependencies. Deployed in government and defence environments.
Managed Service
Operated end-to-end by our forensic engineering team. Your enforcement platform, our operational responsibility.
Build your enforcement function
30-minute platform walkthrough. Tailored to your use case. No commitment.